India-ASEAN and East Asia Summit – Strengthening Maritime Security

India-ASEAN and East Asia Summit

India-ASEAN and East Asia Summit Latest News

  • At the 21st East Asia Summit (EAS) and 23rd ASEAN-India Summit in Manila, the Indian PM announced several initiatives to deepen India's strategic, economic and maritime engagement with Southeast Asia. 
  • The initiatives focus on maritime security, freedom of navigation, cybersecurity, critical minerals, disaster management and people-to-people connectivity.
  • The announcements reflect India's commitment to a free, open, inclusive and rules-based Indo-Pacific and its broader Act East Policy.

Seafarers’ Safety and Maritime Security

  • Seafarers' safety initiative: India launched an initiative among EAS members (11 ASEAN countries + 8 dialogue partners = ASEAN Plus) to strengthen cooperation in joint training and emergency response for seafarers.
  • Growing maritime threats: 
    • Commercial ships carrying Indian nationals have faced attacks amid conflicts in the Strait of Hormuz and Black Sea. 
    • At least 22 Indian nationals have reportedly been killed since the US-Israel war against Iran began in February 2026.
  • Maritime cooperation: The Indian PM proposed a long-term ASEAN-India maritime cooperation plan covering -
    • Maritime connectivity and scientific research.
    • Disaster management and Coast Guard cooperation.
    • Maritime Domain Awareness (MDA).
    • Seafarers' safety and security.
  • Significance: The initiative seeks to protect maritime trade routes, ensure freedom of navigation and strengthen collective responses to emerging maritime threats.

East Asia Summit - Addressing Emerging Security Challenges

  • The PM highlighted multiple challenges affecting regional stability -
    • Geopolitical conflicts: Conflicts are disrupting global supplies of food, fuel and fertilisers.
    • Maritime insecurity: Ships and seafarers are increasingly vulnerable to attacks on international waterways.
    • Terrorism and transnational crime: Cyber fraud, online scams and other forms of cross-border crime are emerging security threats.
  • He emphasised that the world needs peace, stability and predictability, with dialogue, mutual respect and cooperation forming the foundation of international relations.
  • India reiterated its support for peaceful resolution of conflicts, including those in Ukraine and West Asia.

Digital Security and Cybercrime Cooperation

  • Recognising the growing threats in the digital domain, India proposed -
    • EAS cyber crime conference: To be hosted at India's National Forensic Sciences University for regional cooperation and capacity building.
    • Joint cyber forensics training: To strengthen investigative capabilities and facilitate knowledge-sharing among ASEAN countries.
    • Combating online scams: EAS leaders issued a joint statement on addressing online scams and cyber-enabled criminal activities.
    • Responsible AI: India advocated human-centric, inclusive and safe Artificial Intelligence.
    • Digital watermarking: Promoted as a technological tool to counter deepfakes and misinformation.
  • Significance: These initiatives seek to strengthen regional digital trust, cyber resilience and cooperation against transnational cybercrime.

Strengthening India-ASEAN Strategic Partnership

  • The Indian PM reiterated that ASEAN unity and centrality are at the heart of India's Act East Policy.
  • Key developments include -
    • India-ASEAN relations have expanded beyond historical and cultural connections into digital technology, defence and space.
    • The Comprehensive Strategic Partnership will be further strengthened to promote a secure, inclusive and prosperous Indo-Pacific.
    • ASEAN Community Vision 2045 and Viksit Bharat 2047 offer opportunities for aligning regional development priorities.
    • India and ASEAN together represent nearly one-fourth of the global population, highlighting the importance of cooperation over competition.
  • New areas of cooperation: India proposed several initiatives to expand sectoral cooperation, like,
    • Tourism: Free e-visas for ASEAN tourists visiting India.
    • Nuclear energy: Technical exchanges and cooperation.
    • Critical minerals. Cooperation in mining and critical mineral supply chains.
    • Space: Joint space hackathon.
    • Youth engagement: Youth summit, young parliamentarian exchanges and start-up hackathons.
    • Education: Enhanced scholarships for ASEAN students at Nalanda University.
    • Disaster management: Adoption of an ASEAN-India joint statement on disaster management.

Strengthening Cultural and Regional Engagement

    • India emphasised its shared civilisational heritage with Southeast Asia.
  • For example,
      • National Maritime Heritage Complex, Lothal: Being developed to showcase India's maritime history and its historical connections with the region.
      • EAS University Heads Conclave: To be organised at Nalanda to promote cooperation in education and research.
  • Progress in India-ASEAN relations:
    • Since 2014, India has undertaken several initiatives to strengthen regional engagement, for example, nearly 250 Quick Impact Projects (QIPs), over 10,000 skill-development scholarships, etc.
    • The adoption of the ASEAN-India joint statement on disaster management further reinforces cooperation in regional resilience.

Way Forward

  • Rules-based order: Uphold UNCLOS principles, freedom of navigation and peaceful settlement of maritime disputes.
  • Economic integration: Enhance trade, investment, connectivity and resilient critical-mineral supply chains.
  • Digital resilience: Develop common frameworks for cybercrime investigation, AI governance and digital trust.
  • Institutional cooperation: Translate summit-level commitments into time-bound projects with measurable outcomes.
  • People-to-people ties: Expand educational exchanges, tourism, youth engagement and cultural diplomacy.

Conclusion

India's expanding engagement with ASEAN and EAS reflects its ambition to emerge as a reliable regional partner and a key pillar of Indo-Pacific stability. 

Source: IE

India-ASEAN and East Asia Summit FAQs

Q1: How does maritime security strengthen India's Act East Policy?

Ans: It ensures freedom of navigation and strengthens India's strategic engagement with ASEAN and the wider Indo-Pacific.

Q2: What is the significance of the Seafarers' Safety Initiative launched at the EAS?

Ans: It promotes joint training, emergency response and regional cooperation.

Q3: How can India-ASEAN cooperation address emerging cybersecurity threats?

Ans: Through joint cyber forensics training, information-sharing and cooperation against online scams.

Q4: What is the significance of ASEAN unity and centrality for India's Indo-Pacific vision?

Ans: It provides an inclusive regional framework for maintaining a free, open and rules-based Indo-Pacific.

Q5: How can India-ASEAN cooperation contribute to regional economics?

Ans: Cooperation in critical minerals, education, tourism, etc., can promote economic integration, innovation and P2P connectivity.
Responsible Microfinance in India: RBI’s Push Against Pseudo Consent and Debt

Responsible Microfinance in India

Responsible Microfinance Latest News

  • The Reserve Bank of India (RBI) has taken a firm stand on the microfinance sector, signalling that financial inclusion cannot come at the cost of household over-indebtedness, and that responsible lending must begin before a loan is even sanctioned. 
  • After two years of contraction, India’s microfinance sector — which primarily serves unbanked households, informal workers, and rural populations near the poverty line — shows signs of stability, though recovery remains fragile.

Current State of the Microfinance Sector

  • Early-stage delinquency (30-179 days past due) dropped sharply to 1.9% in June 2026, from 6.1% a year earlier.
  • However, loans overdue by more than 180 days remained high at 17.4% — indicating persistent legacy stress.
  • SIDBI-Equifax Microfinance Pulse Report (June 2026): 
    • Outstanding portfolio fell 12% YoY to ₹2.69 lakh crore.
    • 7.15 crore active loan accounts.
    • Disbursements (April-June 2026) grew 17% YoY to ₹62,302 crore.
  • Banks’ direct microfinance exposure: ~₹83,080 crore — about 25% of industry portfolio, but under 0.4% of total scheduled commercial bank credit (per MFIN data).
  • Economic significance: Despite a small direct financial footprint, microfinance substantially influences rural consumption, women’s entrepreneurship, and informal businesses. Its contribution to India’s Gross Value Added (GVA) was 2.03% in 2018-19, projected to rise to 2.7% by 2025-26.

Industry’s Key Demands

  • Revise the Income Eligibility Threshold
    • The current ₹3 lakh annual household income threshold (introduced in 2022) is seen by MFIN as outdated, failing to reflect rising wages and inflation.
    • Risk: Borrowers with marginally improved incomes may fall outside the regulatory definition, even though they still need small-ticket credit.
  • Review the Fixed-Obligation-to-Income Ratio (FOIR)
    • Industry wants a review of the uniform 50% FOIR cap, arguing it doesn’t account for regional variations in income, cost of living, and repayment capacity.
    • Some propose assessing only the interest component of certain loans, rather than full principal + interest repayment.
  • Consistent Loan Classification
    • MFIN seeks uniform reporting of all eligible microfinance loans under the microfinance category in credit-information company databases, flagging current inconsistencies.
  • Underlying concern: Continued regulatory uncertainty over FOIR and eligibility could discourage fresh capital in the sector and push vulnerable households toward informal moneylenders charging higher interest rates.

RBI’s Response: Holding the Line

  • On FOIR: RBI rejected excluding principal repayments, arguing this would understate actual household indebtedness. It cited data showing the average microfinance borrower spends just 18.7% of monthly household income on loan repayment, while two-thirds goes toward consumption.
  • On the income threshold: RBI linked any regulatory flexibility to demonstrable improvements in household income assessment, credit reporting, and responsible lending practices.
  • RBI Deputy Governor emphasised: “It is imperative for the industry to strengthen its lending practices, uphold responsible credit standards and build greater resilience.”
  • The RBI faces a genuine balancing act — ensuring credit discipline doesn’t become a barrier to financial inclusion, while not letting lax standards undermine microfinance’s core purpose.

Understanding “Pseudo Consent”

  • RBI has distinguished between genuine, informed consent and “pseudo-consent” — where borrowers sign documents without adequately understanding their contents.
  • Mandatory requirement: Lenders must provide a Key Facts Statement (KFS), explain it in a language the borrower understands, and obtain acknowledgment of genuine understanding.
  • Why this matters now: With expanding digital lending, instant personal loans, and credit cards, pseudo-consent risks becoming a wider banking-sector problem, not just a microfinance issue.
  • Broader economic context: Elevated crude oil prices, costlier transportation, and high inflation can squeeze household disposable incomes — pushing additional borrowing. Without safeguards, financial inclusion could paradoxically deepen indebtedness rather than build resilience.

The Conflict-of-Interest Problem

  • India’s two RBI-recognised Self-Regulatory Organisations (SROs) — MFIN and Sa-Dhan — are industry associations whose own members are the institutions they’re meant to monitor.
  • Microfinance Institutions (MFIs) also market additional products (insurance, savings-linked schemes) alongside credit — creating potential conflict between borrowers’ actual needs and institutions’ revenue interests.
  • Core tension: MFIs are meant to provide affordable credit to underserved households, but profit and portfolio-growth pressures can drive aggressive lending.

The Way Forward: RBI’s Regulatory Ethos

  • RBI’s June 2026 directions on advertising, marketing, and sale of financial products aim to prohibit deceptive practices and ensure explicit customer consent.
  • These rules take effect from January 1, 2027.
  • Core message: The era of prioritising loan growth over borrower protection must end — MFI success should be measured by borrowers’ financial resilience, not disbursement volumes.

Conclusion

  • The RBI’s firm stance reflects a crucial recalibration: financial inclusion must be measured not by credit volume, but by borrowers’ genuine financial resilience. 
  • As India’s microfinance sector seeks regulatory flexibility, embedding informed consent, consistent credit assessment, and accountability will determine whether microfinance remains a tool for empowerment — or inadvertently becomes a pathway to deeper household debt.

Source: TH

Responsible microfinance FAQs

Q1: Why is responsible microfinance in India a priority for the RBI?

Ans: Responsible microfinance in India is essential to expand financial inclusion without exposing vulnerable households to excessive borrowing, repayment stress and unsustainable debt.

Q2: What is pseudo-consent in microfinance lending?

Ans: Responsible microfinance in India requires genuine informed consent, as pseudo-consent occurs when borrowers sign loan documents without adequately understanding their terms and obligations.

Q3: Why has the RBI rejected changes to the FOIR calculation?

Ans: Responsible microfinance in India requires realistic debt assessment; the RBI rejected excluding principal repayments because doing so would underestimate borrowers’ actual indebtedness.

Q4: What conflict-of-interest concerns exist within the microfinance sector?

Ans: Responsible microfinance in India faces conflicts because industry associations monitor member institutions, while lenders may promote additional financial products alongside loans.

Q5: What measures can strengthen responsible microfinance in India?

Ans: Responsible microfinance in India can improve through transparent loan disclosures, borrower-understood Key Facts Statements, stronger credit assessment, accountability and protection against deceptive marketing.

Quad Summit 2026 – Maritime Security, AI and Critical Minerals

Quad Summit 2026

Quad Summit 2026 Latest News

  • The leaders of India, the United States, Japan and Australia announced a series of initiatives on maritime security, artificial intelligence, cybersecurity, critical minerals and business cooperation at the Quad Leaders' Meeting held in Manila on the sidelines of the East Asia Summit.

About QUAD 

  • The Quadrilateral Security Dialogue (Quad) is a strategic partnership comprising India, the United States, Japan and Australia. 
  • It seeks to promote a free, open, stable and prosperous Indo-Pacific through cooperation in maritime security, economic resilience, critical and emerging technologies, infrastructure, health and disaster response.
  • The grouping was first initiated in 2007 but became inactive for several years before being revived in 2017 on the sidelines of the ASEAN meeting in Manila. 
  • Although it is not a formal military alliance, the Quad provides a platform for its four members to coordinate on regional and global challenges.
  • Its central objective is to uphold a rules-based international order, promote freedom of navigation and overflight, strengthen regional resilience and oppose coercive actions that undermine Indo-Pacific stability.

Key Outcomes of the 2026 Quad Leaders' Meeting

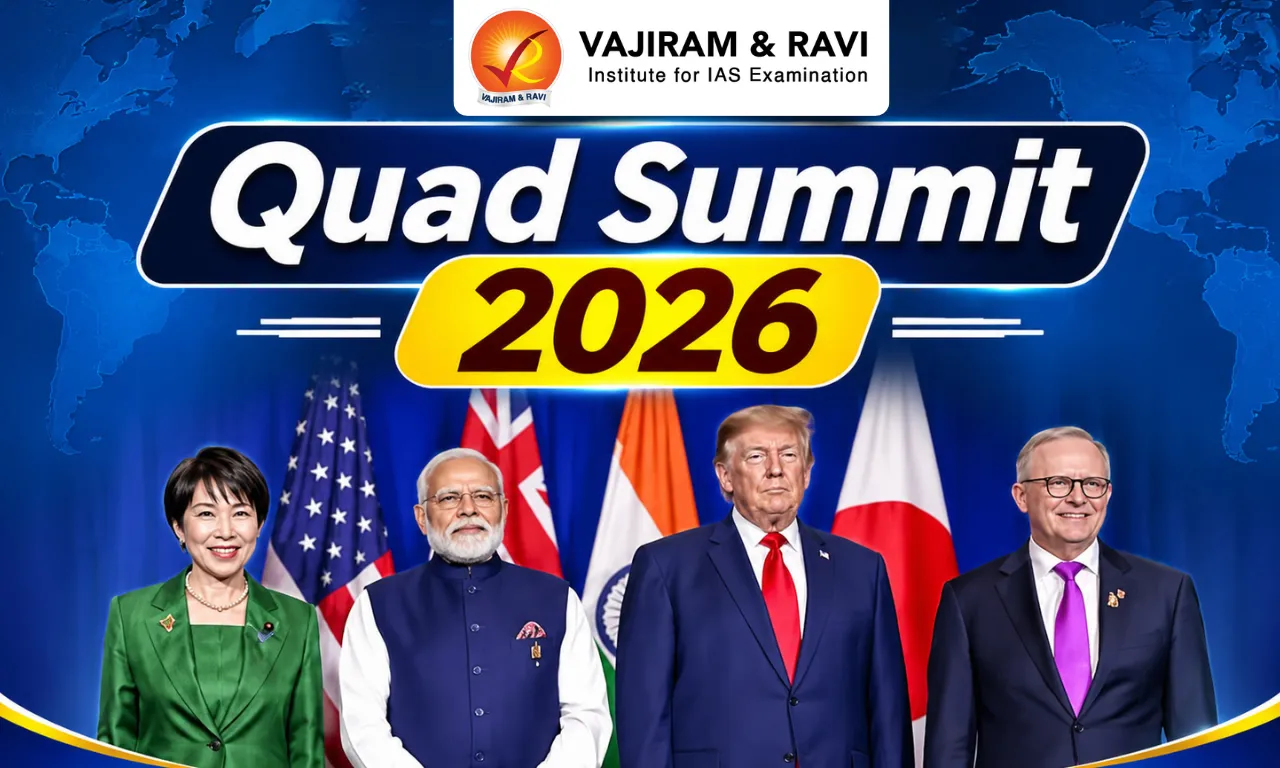
  • The meeting brought together Indian Prime Minister Narendra Modi, US President Donald Trump, Japanese Prime Minister Sanae Takaichi and Australian Prime Minister Anthony Albanese. It was the first Quad leaders' meeting since 2024.
  • The leaders announced several initiatives to deepen cooperation across security, economic and technological domains.
  • Maritime Security and Surveillance Cooperation
    • The leaders announced the Indo-Pacific Maritime Surveillance Collaboration, an initiative aimed at improving information sharing and maritime domain awareness across the region.
    • Under this initiative, patrol aircraft from the four countries are scheduled to participate in a maritime exercise in 2027. The P-8 and P-3C aircraft are expected to fly together in an exercise for the first time in a Quad context.
    • The initiative seeks to strengthen maritime monitoring, improve coordination and ensure safer maritime transit corridors across the Indo-Pacific.
    • The leaders also highlighted the importance of the annual Malabar Naval Exercise, whose 30th edition was recently conducted near Japan. The exercise involved anti-submarine and anti-surface warfare drills, reflecting the growing importance of coordinated maritime capabilities.
  • Quad Business Leaders' Forum
    • The leaders announced the inaugural Quad Business Leaders' Forum, scheduled to be held in Mumbai in early 2027.
    • The forum will bring together business leaders, government officials and policy experts from the four countries to strengthen private-sector cooperation. It will focus on promoting commercial agreements, investment opportunities and business partnerships across the Indo-Pacific.
    • The initiative is intended to complement strategic cooperation with stronger economic and commercial engagement.
  • Artificial Intelligence Cooperation
    • The Quad announced a new Quad AI Accelerator to coordinate and fund efforts supporting trusted artificial intelligence access, deployment and technical assistance across the Indo-Pacific.
    • The initiative seeks to expand access to reliable AI ecosystems and promote cooperation in emerging technologies among countries that share common interests and values.
    • The United States also announced an investment of more than US$85 million to expand access to trusted AI ecosystems across the region.
    • The initiative reflects the Quad's growing emphasis on technological cooperation and the importance of ensuring that emerging technologies contribute to regional economic growth and resilience.
  • Enhanced Cybersecurity Cooperation
    • Recognising the rapid increase in the number and scale of cyber incidents across the region, the leaders announced enhanced Quad Cybersecurity Cooperation.
    • The initiative aims to strengthen collaboration among member countries to promote an open, secure and resilient cyberspace.
    • Cybersecurity has become an important component of regional security, given the growing dependence on digital infrastructure, communication networks and interconnected economic systems.
  • Critical Minerals and Supply Chain Resilience
    • The leaders highlighted the importance of securing critical mineral supply chains and reducing dependence on individual foreign suppliers.
    • Critical minerals and rare earth elements are essential for electric vehicles, renewable energy technologies, semiconductors, defence equipment and advanced manufacturing.
    • The joint statement expressed concern over economic coercion, including arbitrary export restrictions, and emphasised the need to develop secure and diversified supply chains.
  • Counterterrorism and Regional Security
    • The Quad leaders unequivocally condemned terrorism and violent extremism in all their forms and manifestations, including cross-border terrorism.
    • They also committed to strengthening ongoing cooperation on counterterrorism.
    • The joint statement also opposed destabilising or unilateral actions aimed at changing the status quo through force or coercion.

Significance for India

  • The latest initiatives offer India opportunities to strengthen its strategic partnerships while advancing its economic and security interests.
  • Maritime security: Greater information sharing and surveillance cooperation can strengthen India's maritime domain awareness in the Indian Ocean and wider Indo-Pacific.
  • Critical minerals: Diversified supply chains can support India's electric mobility, renewable energy, electronics and defence manufacturing sectors.
  • Technology development: Cooperation in AI and cybersecurity can improve access to trusted technologies and strengthen India's digital capabilities.
  • Economic partnerships: Hosting the inaugural Quad Business Leaders' Forum in Mumbai can create opportunities for Indian businesses and investors.
  • Counterterrorism: The explicit condemnation of cross-border terrorism reinforces India's longstanding diplomatic position.

Source: IE

QUAD Summit 2026 FAQs

Q1: What is the Quad?

Ans: The Quad is a strategic partnership comprising India, the United States, Japan and Australia, aimed at promoting a free, open and stable Indo-Pacific.

Q2: When was the Quad established?

Ans: The grouping was first initiated in 2007 and revived in 2017 on the sidelines of the ASEAN meeting in Manila.

Q3: What is the Indo-Pacific Maritime Surveillance Collaboration?

Ans: It is a Quad initiative to improve information sharing and maritime domain awareness. It includes plans for P-8 and P-3C patrol aircraft to participate in a maritime exercise in 2027.

Q4: What is the Quad AI Accelerator?

Ans: It is an initiative to coordinate and fund efforts supporting trusted AI access, deployment and technical assistance across the Indo-Pacific.

Q5: Where and when will the first Quad Business Leaders' Forum be held?

Ans: It is scheduled to be held in Mumbai in early 2027.

Cold Chain Cybersecurity in India: Lessons from Europe’s Supermarket Fridge Hacks

Cold chain cybersecurity

Cold Chain Cybersecurity Latest News

  • Overnight on October 11-12, 2026, hackers seized control of refrigeration systems at ~700 retail sites in France, spiking temperatures to melt ice off cooling coils, spoiling food, and triggering at least 15 fires, as per France’s cybersecurity agency ANSSI. 
  • A second wave in early November hit stores across eight European countries. Separately, an attack on a refrigeration equipment supplier affected three sites of France’s national blood service — though alarms allowed staff to save blood products in time. 
  • These incidents expose a critical vulnerability: as refrigeration goes digital, it becomes a cybersecurity target, with direct implications for India’s own cold chain infrastructure.

Who’s Behind the Attacks?

  • Recently, France accused Shahid Kaveh, a unit linked to Iran’s Revolutionary Guard Corps (IRGC), of orchestrating the October attacks — a charge Iran has denied.
  • Authorities have not confirmed the same group carried out the subsequent attacks.
  • Separately, cybersecurity firm Lupovis detected suspicious activity against simulated refrigeration controllers (honeypots) between October 20-30, with 250+ login attempts from 91 sources, possibly linked to a Russian state-sponsored group (which Russia denies), though attribution remains unconfirmed.

How Cold Storage Systems Actually Work

  • A cold-storage facility is essentially a large, insulated refrigerator, often divided into rooms at different temperatures.
  • Cooling relies on a refrigerant that absorbs heat as it circulates through coils, with a compressor releasing that heat outside the cooled space.
  • Sensors continuously monitor temperature, sending data to an electronic controller — often a Programmable Logic Controller (PLC), an industrial computer managing compressors, fans, and pumps.
  • The controller also manages defrost cycles — periodically melting ice buildup on coils, which otherwise obstructs airflow and reduces efficiency.

Why Connect Refrigerators to the Internet?

  • Traditionally, staff manually checked and recorded temperatures.
  • Internet connectivity — part of the Internet of Things (IoT) — allows businesses to: 
    • Monitor temperatures and performance remotely, in real time.
    • Receive alerts before stock spoils.
    • Diagnose faults and manage multiple sites from a single system.
    • Allow authorised staff/vendors to adjust settings remotely (temperature, alarms, defrost cycles).
  • Trade-off: Improved efficiency and response times, but increased cyber risk if controllers are poorly secured.

How Attackers Exploit Refrigeration Systems

  • Controllers become vulnerable when directly exposed to the internet or accessed via poorly secured remote connections.
  • Attackers exploit weak/default passwords or outdated software vulnerabilities.
  • Critical risk: Attackers can pivot from corporate IT networks into Operational Technology (OT) systems controlling physical equipment — a pattern seen repeatedly in past security incidents.
  • Equipment lifespan problem: Unlike laptops (replaced every 3-5 years), refrigeration equipment can run for 15-20 years — often well past the point manufacturers stop providing security updates, even though it remains mechanically functional.

Potential Impact on Food Supply Chains

  • Farmers risk income loss if produce spoils or cannot be collected.
  • Food processors, retailers, and logistics companies face stock losses and supply delays.
  • Consumers could face shortages or price hikes.
  • Expert assessment: A single facility attack is unlikely to cause a nationwide food crisis, but disruption to a major distribution hub could affect multiple cities/regions — especially if several facilities share the same refrigeration vendor/platform, turning one vulnerability into a wider cascading failure.

What This Means for India’s Cold Chain

  • As per a February 2026 Rajya Sabha response, India has 8,831 cold-storage facilities with combined capacity of ~40.3 million metric tonnes.
  • Risk concentration: Facilities using internet-connected refrigeration, remote monitoring, and external vendor access are most exposed — including: 
    • Organised retail chains
    • Dairy chilling facilities
    • Pharmaceutical warehouses and vaccine storage centres
    • Large distribution hubs
    • Refrigerated transport using connected fleet-management systems
  • Lower-risk segment: Traditional potato cold storage facilities are less exposed, as their equipment is mostly locally controlled, not internet-connected.

Who’s Responsible for Securing These Systems?

  • Security is a shared responsibility across equipment manufacturers, software providers, system integrators, maintenance contractors, and operating businesses.
  • Manufacturers: Responsible for secure equipment and timely software updates.
  • Operators: Must monitor connected devices and control access.
  • For older equipment without updates, experts recommend restricting access rather than mandatory replacement.
  • Global regulatory reference points: UK/EU network and information security rules, and the EU Cyber Resilience Act’s requirements for product suppliers.

India’s Current Policy Framework — and Its Gaps

  • The National Centre for Cold-chain Development (NCCD)’s Engineering Guidelines & Minimum System Standards (2025) encourage IoT-based monitoring and unified control systems for government-funded facilities.
  • Key gap: These guidelines do not specify detailed cybersecurity requirements — such as secure remote access, network separation, authentication, or update protocols.
  • Separately, CERT-In’s May 2026 cybersecurity blueprint identifies Operational Technology (OT) and cyber-physical systems as priority protection areas, recommending restricted remote access, third-party vendor monitoring, and supply-chain risk management.

Recommended Safeguards

  • Strong passwords and multi-factor authentication.
  • Keep critical controllers off the public internet.
  • Deploy independent temperature sensors and alarms (as proved vital in the French blood-service case).
  • Maintain manual monitoring procedures as backup if automated controls fail.
  • Policy-level recommendation: Incorporate cybersecurity requirements into cold-chain infrastructure standards and government funding conditions, with regular security assessments for facilities storing essential food and medical products.

Conclusion

  • The European fridge hacks reveal how digitising critical infrastructure, without matching cybersecurity investment, creates new vulnerabilities with real-world consequences — spoiled food, fires, and endangered medical supplies. 
  • As India expands IoT-based cold-chain automation, embedding robust cybersecurity standards into infrastructure guidelines and funding conditions is essential to prevent similar disruptions to its food and healthcare supply chains.

Source: IE

Cold Chain Cybersecurity FAQs

Q1: Why do Europe’s supermarket refrigeration attacks raise concerns about cold chain cybersecurity in India?

Ans: Cold chain cybersecurity in India matters because connected refrigeration systems could face similar attacks, risking food spoilage, fires and disruption of essential supply chains.

Q2: How do internet-connected refrigeration systems operate?

Ans: Cold chain cybersecurity in India requires understanding PLCs, sensors and controllers that monitor temperatures and remotely manage compressors, fans and defrost cycles.

Q3: How can hackers exploit refrigeration systems?

Ans: Cold chain cybersecurity in India is threatened by exposed controllers, weak passwords, outdated software and insecure remote connections that allow attackers to manipulate refrigeration operations.

Q4: Which Indian facilities are particularly vulnerable to refrigeration cyberattacks?

Ans: Cold chain cybersecurity in India is crucial for organised retail, dairy chilling facilities, pharmaceutical warehouses, vaccine storage centres, distribution hubs and refrigerated transport networks.

Q5: What measures can strengthen India’s cold-chain cybersecurity?

Ans: Cold chain cybersecurity in India requires strong authentication, restricted internet access, independent temperature alarms, manual monitoring, regular assessments and cybersecurity standards for connected infrastructure.

Enquire Now