Social Security Boards for Gig Workers: Composition, Functions and Benefits

Social Security Boards

Social Security Boards Latest News

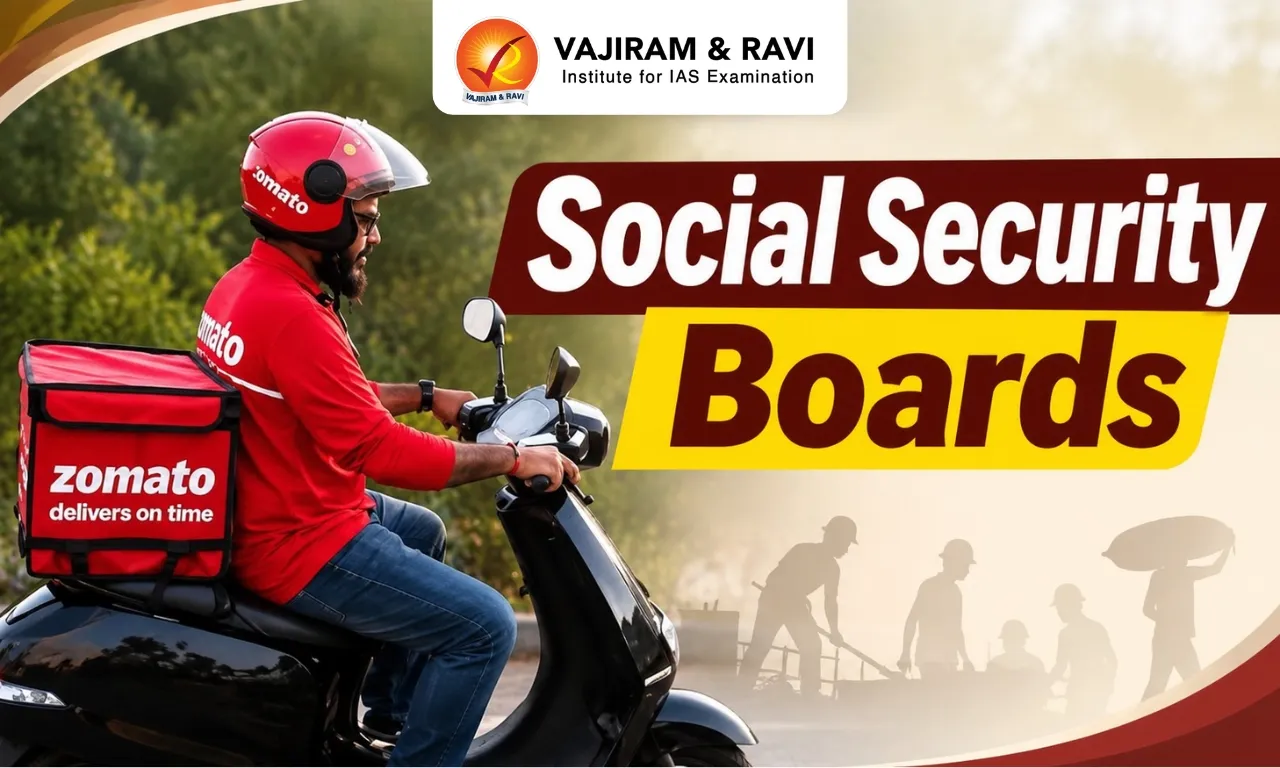
  • The Ministry of Labour and Employment has notified the constitution of two key bodies: the National Social Security Board (NSSB) for unorganised workers (40 members) and a separate NSSB for gig and platform workers (22 members). 
  • Both boards are tasked with designing, monitoring, and recommending welfare schemes to bridge India’s long-standing social security gap for workers outside the formal employment structure.

Background: The Code on Social Security

  • Notified last year (November 2025), alongside three other labour codes, the Code on Social Security merged nine existing social security laws to cover both organised and unorganised sectors.
  • For the first time, the Code legally defined “gig workers” and “platform workers.”
  • It mandated a national registration system and a dedicated social security fund for unorganised and gig workers.

Composition of the Boards

  • National Social Security Board (Unorganised Workers) — 40 members:
    • Chairperson: Union Minister for Labour and Employment
    • Vice-Chairperson: Secretary, Ministry of Labour and Employment
    • Includes employee and employer representatives.
    • Nominated Members:
      • Unorganised sector workers: 7 representatives representing workers in the unorganised sector
      • Employers of unorganised sector: 7 representatives representing employers
      • Eminent persons from civil society: 7 representatives
      • Parliamentary representatives: 2 members representing the Lok Sabha and 1 member representing the Rajya Sabha (3 total)
      • Central Government Ministries and Departments: 10 members representing concerned central ministries and departments
      • State Governments: 5 members representing State Governments
      • Union Territories: 1 member representing the Union territories [1, 2]
  • National Social Security Board (Gig and Platform Workers) — 22 members:
    • Union Labour Minister chairs it; Labour Secretary serves as Vice-Chairperson (same structure as the unorganised workers’ board).
    • Industry representation: Aggregators and quick-commerce operators like Eternal (Zomato’s parent), Zepto, Swiggy, and Urban Company.
    • Worker representation: BMS, the Indian Federation of App-Based Transport Workers (IFAT), and the National Front of Indian Trade Unions (NFITU).

Functions and Powers of the Boards

  • As per the Code, the NSSB must meet at least thrice a year.
  • Core mandate: Recommend that the Central government frame suitable schemes for different categories of unorganised, gig, and platform workers.

Key Responsibilities

  • Monitor social welfare schemes for unorganised workers.
  • Review expenditure from the social security fund and its accounts.
  • Review record-keeping functions related to gig workers’ welfare schemes performed at the state level.
  • Advise the Central government on matters arising from administering the Code.
  • Undertake other functions as assigned by the Central government from time to time.

The Social Security Fund: Who Pays, and for What?

  • The Code envisions a Social Security Fund for gig and platform workers, funded through: 
    • Central and State government contributions.
    • Corporate Social Responsibility (CSR) funds.
    • Fines collected through compounding.
  • Aggregator Contributions: Companies like Amazon, Flipkart, Swiggy, and Zomato must contribute 1-2% of their annual turnover to the fund — with total contribution capped at 5% of the amount payable to workers.
  • Covered benefits the Centre may frame schemes for include: 
    • Life and disability cover.
    • Accident insurance.
    • Health and maternity benefits.
    • Old age protection.
    • Crèche facilities.

Expanded EPFO Coverage: A Major Structural Shift

  • EPFO (Employees’ Provident Fund Organisation) provisions now apply to all establishments with 20+ employees, regardless of industry type.
  • Previously, EPFO applied only to establishments listed in Schedule 1 of the Act — primarily manufacturing sector entities.
  • This restriction has been removed under the Code on Social Security, bringing both organised and unorganised sector workers under the social security umbrella.
  • Schemes will be funded wholly or partly by Central/State governments or CSR contributions.

What Changes for Gig Workers Specifically

  • Gig and platform workers will receive social security cover for the first time in India’s labour history.
  • Mandatory Registration: Platforms must work with the government to register all gig and platform workers.
  • Technology Enabler: Registration will use an Aadhaar-linked Universal Account Number (UAN) — ensuring benefits remain portable across states, crucial given gig workers’ frequent inter-state mobility for work.
  • Scale of Impact: As per NITI Aayog, India’s gig economy is projected to employ 2.35 crore (23.5 million) workers by 2029-30 — making this reform potentially transformative for a rapidly growing workforce segment.

Conclusion

  • The notification of these two Social Security Boards operationalises one of the most significant labour reforms in recent Indian history — extending formal social security protections to a workforce segment that has historically operated entirely outside such safeguards. 
  • By mandating aggregator contributions, enabling portable Aadhaar-linked registration, and expanding EPFO coverage beyond manufacturing-sector limits, the Code addresses a genuine structural gap as India’s gig economy approaches a projected 2.35 crore workers by 2029-30. 
  • However, the real test will lie in implementation — particularly ensuring that board composition remains genuinely representative of worker interests, and that the promised benefits translate into accessible, timely support for a workforce often characterised by precarious, fragmented employment.

Source: IE

Social Security Boards FAQs

Q1: What are the Social Security Boards for Gig Workers?

Ans: Social Security Boards for Gig Workers are statutory bodies tasked with recommending, monitoring and reviewing welfare schemes for gig and platform workers.

Q2: What is the composition of the Social Security Boards for Gig Workers?

Ans: The Social Security Boards for Gig Workers include government officials, worker representatives, employers, industry representatives and other nominated members.

Q3: What are the main functions of the Social Security Boards for Gig Workers?

Ans: Social Security Boards for Gig Workers recommend welfare schemes, monitor implementation, review fund expenditure and advise the Central government on social security matters.

Q4: How will the Social Security Boards for Gig Workers be funded?

Ans: The Social Security Boards for Gig Workers oversee schemes supported by government contributions, CSR funds, compounding fines and mandatory aggregator contributions.

Q5: How will the Social Security Boards for Gig Workers benefit platform workers?

Ans: Social Security Boards for Gig Workers can facilitate life, accident, health, maternity and old-age protection through welfare schemes and Aadhaar-linked portable registration.
Uttarakhand Helicopter Crashes: Causes, Safety Risks and Regulatory Gaps

Uttarakhand Helicopter Crashes

Uttarakhand Helicopter Crashes Latest News

  • A helicopter carrying six people, including the pilot, crashed while returning from Badrinath to Dehradun recently, amid adverse weather conditions — all six confirmed dead. 
  • This latest tragedy has once again spotlighted the safety risks associated with helicopter operations in one of India’s most challenging flying environments, raising urgent questions about India’s helicopter-based pilgrimage tourism.

The Scale of the Problem

  • As per Ministry of Civil Aviation (MoCA) data (shared with Parliament, July 2025): of 12 helicopter accidents nationwide since 2020, 7 occurred in Uttarakhand alone.
  • Fatality statistics are starker: Of 30 total deaths in helicopter crashes during this period, 21 occurred in Uttarakhand.
  • Last summer saw at least 5 incidents within just a couple of months, including multiple fatal crashes — prompting the state administration, UCADA, MoCA, and DGCA to announce safety audits and temporary operational pauses.

Why Uttarakhand’s Terrain Makes Flying So Dangerous

  • Much of the Char Dham route passes through deep valleys surrounded by steep mountains, leaving little room to manoeuvre — especially when weather deteriorates suddenly or technical problems arise.
  • Mountainous terrain disrupts wind patterns, causing sudden turbulence that’s hard to predict.
  • Areas are prone to rapid visibility changes from cloud movement, mist, and unpredictable rain.
  • Helicopters here primarily operate under Visual Flight Rules (VFR) — pilots must fly visually, maintaining visibility and separation from terrain without instrument-based guidance.
  • Key Risk: Controlled Flight Into Terrain (CFIT) — when a pilot-controlled aircraft unintentionally strikes terrain. This was the probable cause in the June 2025 Gaurikund crash, where the helicopter reportedly flew despite poor visibility and extensive clouding.
  • Localised Weather Data Gap: Weather readings at a base like Guptkashi may not reflect actual conditions at Kedarnath or in connecting valleys — a district-level forecast cannot tell a pilot if a specific valley entrance is safe to enter at a given moment.

Regulatory and Air Traffic Management Gaps

  • In narrow mountain valleys with multiple helicopters operating simultaneously, proper air traffic control is critical — but many Uttarakhand helipads lack this infrastructure.
  • Pilots often rely on radio communications and relayed information rather than formal air traffic control.
  • Jurisdictional Divide:
    • DGCA (Directorate General of Civil Aviation) regulates airspace nationally (aviation is a Union List subject).
    • Uttarakhand Civil Aviation Development Authority (UCADA), established 2013, coordinates with helicopter operators at the state level.
  • Parliamentary Standing Committee on Transport, Tourism and Culture (August 2025 report) flagged this starkly: 
    • DGCA’s role is primarily licensing, issuing safety guidelines to UCADA but not exercising direct, continuous supervision over daily operations.
    • This creates jurisdictional ambiguity, with DGCA appearing to have ceded direct oversight of a hazardous aviation activity to a state-level body whose capacity and expertise have been questioned.
    • The Committee called this a symptom of a “larger and more dangerous structural flaw” — a “fractured and ambiguous regulatory command structure” in India’s aviation governance.

Do Commercial Pressures Compromise Safety?

  • Helicopter services have grown alongside religious tourism, offering pilgrims faster, easier access to remote Himalayan shrines.
  • This creates concentrated flight activity during the short pilgrimage season (just a few months annually).
  • High Traffic Volumes Demand: effective coordination, reliable communications, clear departure/arrival procedures, and accurate weather data — gaps in any of these leave pilots managing complexity with inadequate information.
  • During peak demand, helicopters run repeated shuttle trips, and the economics of short-duration operations can incentivise maximising daily trip counts.
  • Expert Concerns: Commercial pressure may encourage flights in poor weather, inadequate technical checks, and continued operations despite warnings.
  • Pilot fatigue is a significant but under-monitored risk — repeated flights in demanding terrain require constant reassessment of conditions, terrain, aircraft performance, and air traffic.
  • A DGCA operations circular governs safety for pilgrimage helicopter flights, placing responsibility on operators -but recurring accidents raise doubts about enforcement effectiveness.

Conclusion

  • Uttarakhand’s helicopter tragedies don’t stem from one single failure. They result from many weaknesses coming together. The terrain is treacherous. 
  • The weather is unpredictable. Local weather forecasting remains inadequate. Air traffic management is fragmented. On top of this, the national regulator’s oversight role stays mostly advisory, not operational.
  • The Parliamentary Standing Committee’s findings point to something deeper. This isn’t just an isolated aviation safety issue. It reflects a broader governance gap. This gap exists between central regulators and state-level implementation bodies.
  • Two things need to change. First, DGCA and UCADA’s roles need clearer separation. Genuine, continuous safety supervision must replace periodic licensing checks. Second, commercial pressures during the pilgrimage season need better balance against safety protocols. 
  • Until both happen, the Himalayan skies above Char Dham will likely remain among India’s most dangerous flying corridors.

Source: IE | TP

Uttarakhand Helicopter Crashes FAQs

Q1: Why are Uttarakhand helicopter crashes a recurring concern?

Ans: Uttarakhand helicopter crashes are a recurring concern because difficult mountain terrain, unpredictable weather, inadequate air traffic management and operational pressures combine to increase flying risks.

Q2: How does Himalayan geography contribute to Uttarakhand helicopter crashes?

Ans: Deep valleys, steep mountains, sudden turbulence and rapidly changing visibility make navigation difficult and leave pilots with limited room to manoeuvre safely.

Q3: What is Controlled Flight Into Terrain in the context of Uttarakhand helicopter crashes?

Ans: Controlled Flight Into Terrain occurs when a functioning aircraft unintentionally strikes terrain, often because poor visibility prevents pilots from recognising nearby obstacles.

Q4: What regulatory gaps contribute to Uttarakhand helicopter crashes?

Ans: Uttarakhand helicopter crashes highlight fragmented oversight, as DGCA primarily issues guidelines while UCADA coordinates state-level operations without continuous direct supervision.

Q5: How can authorities reduce Uttarakhand helicopter crashes during pilgrimage season?

Ans: Authorities can reduce Uttarakhand helicopter crashes through continuous safety supervision, better localised weather data, stronger air traffic control and stricter enforcement of operational protocols.

Binance Hack – Cybersecurity Risks, Cryptocurrency Regulation and Investor Protection

Binance Hack

Binance Hack Latest News

  • Binance, one of the world's largest cryptocurrency exchanges, suffered a cyberattack on October 29, resulting in estimated losses of approximately $6.3 billion and raising concerns about cybersecurity and investor protection in the cryptocurrency sector.

Understanding the Binance Cyberattack

  • Binance is a major global cryptocurrency exchange that facilitates the trading and transfer of digital assets. 
  • The recent cyberattack exposed vulnerabilities in its operational security infrastructure and resulted in the unauthorised withdrawal of cryptocurrency assets.
  • Binance has temporarily paused deposits and withdrawals while conducting security checks. Deposits were subsequently restored.
  • The exchange later estimated the losses at approximately $6.3 billion and initiated efforts to freeze and recover the stolen assets.

How the Hack Took Place

  • According to Binance's initial investigation, the attack may have involved a compromised laptop belonging to a DevOps engineer. 
  • The attacker allegedly used access to a service container to submit unauthorised withdrawal transactions.
  • Binance's co-CEO maintained that the incident was complex and did not involve the misuse of a single engineer's permissions or a simple one-click vulnerability.
  • The company subsequently disclosed additional points of breach. However, it stated that there was no evidence of cryptocurrency wallet private keys being leaked.

Recovery of Stolen Cryptocurrency Assets

  • Following the attack, Binance collaborated with industry partners and blockchain companies to freeze the stolen assets.
  • Approximately $3 billion worth of assets were reported to have been frozen on-chain.
  • Two major stablecoin issuers also participated in the recovery effort:
    • Tether: Its CEO reported that the company had frozen more than 1.567 billion USDT.
    • Circle: Its CEO announced that the company had frozen more than 800 million USDC.
  • Stablecoins are cryptocurrencies designed to maintain a relatively stable value, generally by being pegged to an asset such as the US dollar.
  • Binance also committed to covering the stolen funds through its Secure Asset Fund for Users (SAFU) and corporate treasury. The company stated that approximately $5 billion of the affected assets were already available in the exact token assets involved, while the remaining amount was being acquired through market and over-the-counter (OTC) channels.

Implications for the Cryptocurrency Sector

  • The Binance hack has raised concerns about the security, transparency and regulatory oversight of cryptocurrency exchanges.
  • Cybersecurity and Operational Vulnerabilities
    • The alleged compromise of an employee's laptop highlights the risks associated with internal access privileges, endpoint security and third-party or operational infrastructure.
    • Even when private keys remain secure, vulnerabilities in connected systems can expose exchanges to large-scale financial losses.
  • Market Volatility
    • Major cryptocurrency hacks often trigger investor anxiety and uncertainty. Following the incident, Bitcoin, Ethereum's Ether and Binance-linked BNB experienced noticeable, although not drastic, price declines.
    • Such reactions demonstrate how security incidents involving major exchanges can affect confidence across the wider digital-asset market.
  • Investor Protection and Regulatory Oversight
    • Cryptocurrency markets operate under varying regulatory frameworks across jurisdictions. Investors may have limited legal protections and face difficulties recovering funds when exchanges experience cyberattacks or operational failures.
    • The incident also adds to Binance's existing regulatory challenges. In 2023, the US Treasury announced historic settlements with the exchange over failures to prevent and report suspicious transactions involving terrorist organisations, ransomware attackers, money launderers and other sanctioned or criminal actors.
    • A cyberattack resulting in billions of dollars in losses could further complicate the exchange's regulatory and operational environment.

Key Challenges in Cryptocurrency Security

  • The incident highlights several structural concerns affecting the digital-asset ecosystem:
    • Centralised vulnerabilities: Large exchanges hold and process substantial volumes of digital assets, making them attractive targets for cybercriminals.
    • Insider and access risks: Compromised employee devices and excessive access privileges can create entry points for attackers.
    • Cross-border investigations: Cryptocurrency transactions can move rapidly across international jurisdictions, complicating the tracing and recovery of stolen assets.
    • Regulatory fragmentation: Differences in national laws and enforcement mechanisms create gaps in oversight.
    • Limited investor recourse: Investors may face uncertainty over compensation, liability and dispute resolution following major security incidents.

Way Forward

  • Strengthening cryptocurrency security requires coordinated action by exchanges, regulators, technology providers and law enforcement agencies.
  • Stronger access controls: Exchanges should adopt multi-factor authentication, least-privilege access and continuous monitoring of employee devices and systems.
  • Independent security audits: Regular penetration testing, vulnerability assessments and third-party audits can help identify weaknesses before they are exploited.
  • Transaction monitoring: Exchanges should strengthen real-time detection of unusual withdrawals and suspicious blockchain activity.
  • Regulatory cooperation: Cross-border information-sharing and coordinated investigations are essential for tracing stolen digital assets.
  • Investor safeguards: Exchanges should maintain transparent asset-reserve disclosures, robust recovery mechanisms and clear compensation policies.
  • Incident transparency: Timely disclosure of breaches and detailed technical investigations can help restore investor confidence and improve industry-wide security standards.

Source: TH

Binance Hack FAQs

Q1: What happened in the Binance hack?

Ans: Binance suffered a cyberattack on October 29, resulting in estimated cryptocurrency losses of approximately $6.3 billion. The initial investigation suggested that a compromised employee laptop may have enabled unauthorised withdrawal transactions.

Q2: Who was responsible for the Binance hack?

Ans: The attackers had not been independently confirmed. Blockchain analytics firm Chainalysis attributed the attack with a high degree of confidence to North Korean-linked cybercriminals associated with the TraderTraitor group.

Q3: What is Binance's SAFU fund?

Ans: The Secure Asset Fund for Users (SAFU) is an emergency reserve established by Binance to protect users in certain exceptional circumstances. The exchange committed to using it alongside its corporate treasury to cover the stolen funds.

Q4: What are stablecoins?

Ans: Stablecoins are cryptocurrencies designed to maintain a relatively stable value by being linked to assets such as the US dollar.

Q5: How did Tether and Circle respond to the attack?

Ans: Tether reported freezing more than 1.567 billion USDT, while Circle reported freezing more than 800 million USDC linked to the incident.

Enquire Now